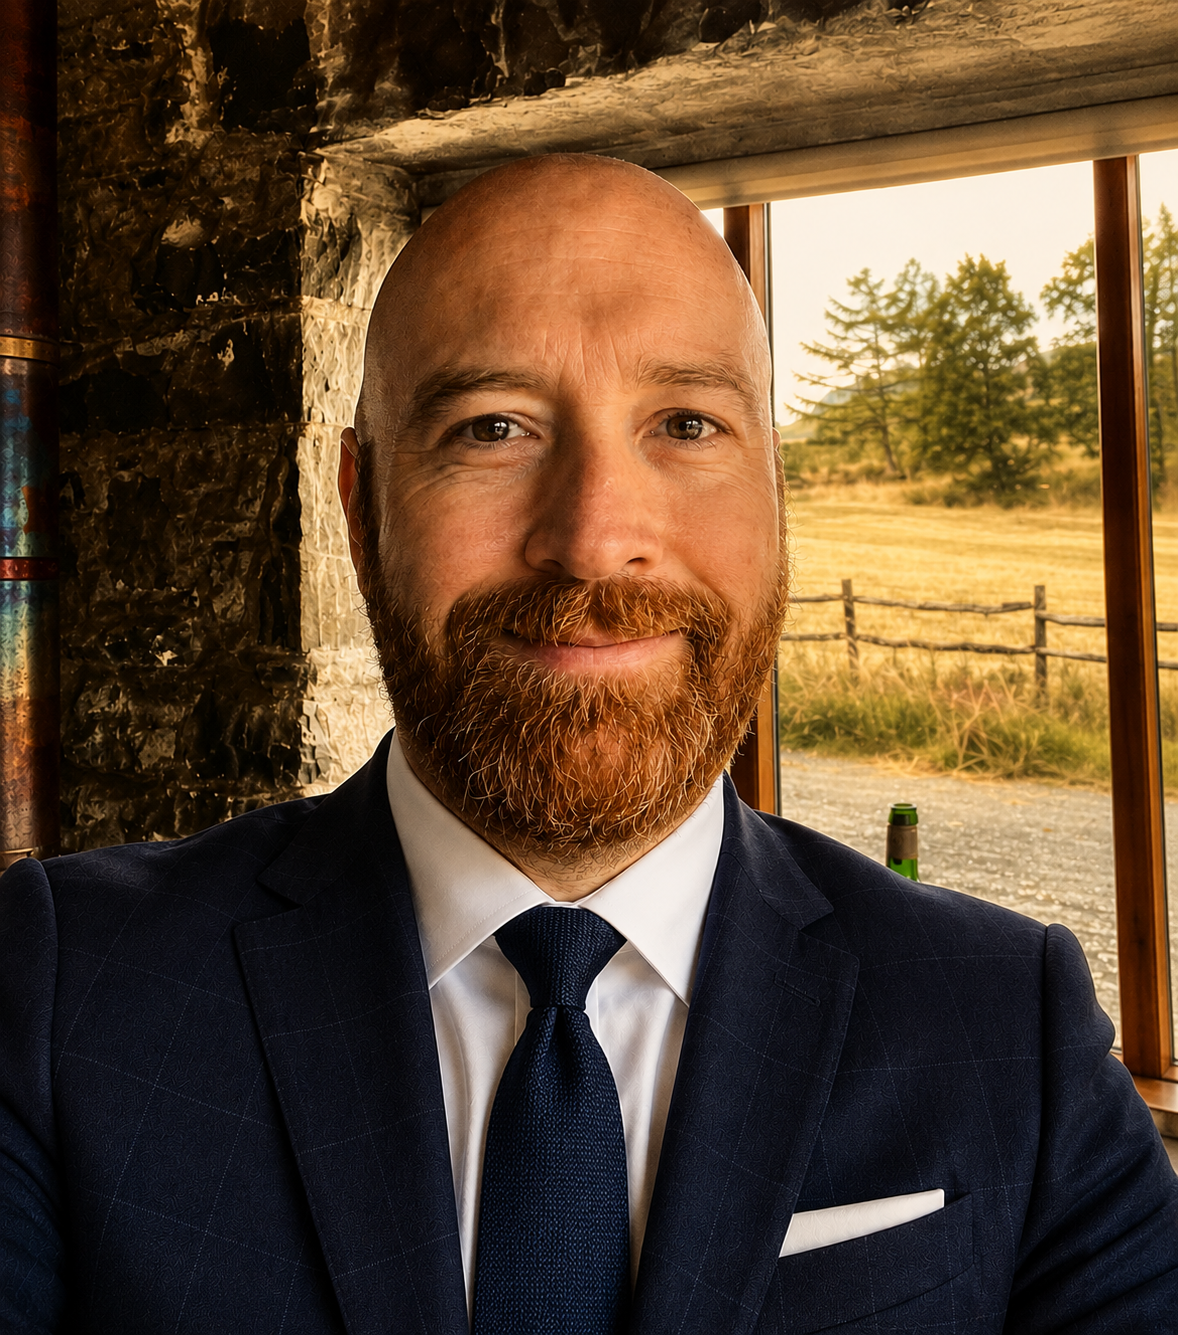
About Owen Ocean
Governance grounded in technical experience.
Owen’s route into cyber leadership began in infrastructure engineering and management, followed by technical architecture and consultancy.
That background shapes Ocean Security’s approach: connect risks and controls to real systems, suppliers, responsibilities and recovery capabilities.
In formal CISO leadership, Owen’s work has covered cyber and technology-risk governance, ISO 27001-aligned controls, risk assessment, audit readiness, supplier assurance, remediation governance, business continuity, disaster-recovery architecture and executive reporting.
Working with Ocean Security
Engagements start with a defined problem, a clear scope and a practical outcome. The aim is to leave leadership and technical teams with documented decisions, owned actions and evidence they can use.
Discuss a project
Tell Owen what needs to change and the outcome you require.
Email owen@oceansecurity.tech or use the Contact page.